Investors Inquiry
Request a Demo

Download Product Brochure
Download Cybeats Marketplace Brochure
Download Product Brochure
SBOM Studio



Software Bill of Materials: SBOM Studio
Gartner estimates that upwards of 80 percent of modern software incorporates open source libraries (OSS) or components from third-party upstream suppliers into product design. These pre-made components increase productivity and shorten development time, but they also introduce risk into the final product. Like any software module, these ingredients can contain vulnerabilities that emerge over time, making the overall software product less secure and reinforcing the need for continuous risk monitoring.

At every stage of the software development lifecycle (SDLC), Cybeats can extract the characteristics and attributes from software SBOM, even without access to source code, to deliver deep insights into the quality and security of software components.
SBOM Studio is the Management Solution for your Software Security Lifecycle
Cybeats SBOM Studio is an enterprise-class solution that helps you understand and track third-party components that are an integral part of your own software. Use SBOM Studio to document what you have and where it came from, and plan for the maintenance that will prevent security posture degradation over the life of your software.

Key Features

Regulations are making SBOMs mandatory, with fines for non-compliance. Manufacturers will have to produce an SBOM for what they ship and hand it to regulators on request. In the US, Section 524B of the FD&C Act already requires one in premarket submissions for cyber devices.
The first step in mitigating these risks is the ability to inspect all the software that comes from suppliers into your supply chains. In industries where safety and security are paramount, it is not economically feasible to manually inspect all third-party files to ensure the quality of a multi-tier software supply chain.
The time is now to develop a business advantage by putting the systems in place to manage and share SBOMs.

Organizations have a need to iterate and deliver software rapidly. A documented SBOM provides the ability to forecast costs for cybersecurity over the product lifecycle and allows the business to properly budget and allocate resources to maintain an advantage over security threats. Customers have reported cutting vulnerability review from a day to under an hour, and saving about 500 hours per project on vulnerability analysis and prioritization for open source projects.

Create transparency and build trust across your software supply chain by sharing SBOMs with customers and receiving SBOMs from technology providers. Immediately understand the risks inherent in your products and mitigate as needed.
Who Needs SBOM Studio?
SBOM Studio gives every level of your organization the view it needs. It provides high level data and metrics for executives and managers and can go deep into the nuts and bolts for software developers. It is built for the software you build and ship, including the third-party components inside it; for software you buy and run, see SBOM Consumer. Who can benefit from using SBOM Studio?

Industrial control system (ICS) environments who need to reduce cyber risk to ICS infrastructure, and gain compliance with ICS cybersecurity standards.

Makers of operational technology (OT) equipment who need to track and patch the software inside every device they ship.

Medical device manufacturers whose premarket submissions for cyber devices must include an SBOM and a plan to monitor and address postmarket vulnerabilities, under Section 524B of the FD&C Act.

Developers, product managers, and security officers who must ensure the secure design and ongoing function of any software product, including code embedded in various hardware devices.

Company executives who want to thoroughly understand the risks inherent in their software products and future costs for maintenance.

Any entity that sells or plans to sell software products, equipment, or devices with embedded software to the U.S. military or a U.S. government agency (compliance with Executive Order 14028).

Enterprises and government agencies that build software in-house and need one record of every product release.

Any team that ships software built on third-party and open source components it does not fully control.
SBOM Studio: frequently asked questions
Answers on how SBOM Studio manages Product Release SBOMs, immutable commits, formats and VEX.

What is SBOM Studio?
An SBOM management platform where the immutable commit is the compliance artifact. It records Product Release SBOMs as immutable commits, shows every component enriched with supply chain intelligence and the vulnerabilities that affect them, and controls who receives the published one.

Do you need an SBOM management platform if you already generate SBOMs?
Yes, because generating was never the hard part. Most teams already generate SBOMs, then park them in a repository, a shared drive or SharePoint and never look at what is inside them again. The file exists, the risk it describes goes unread.
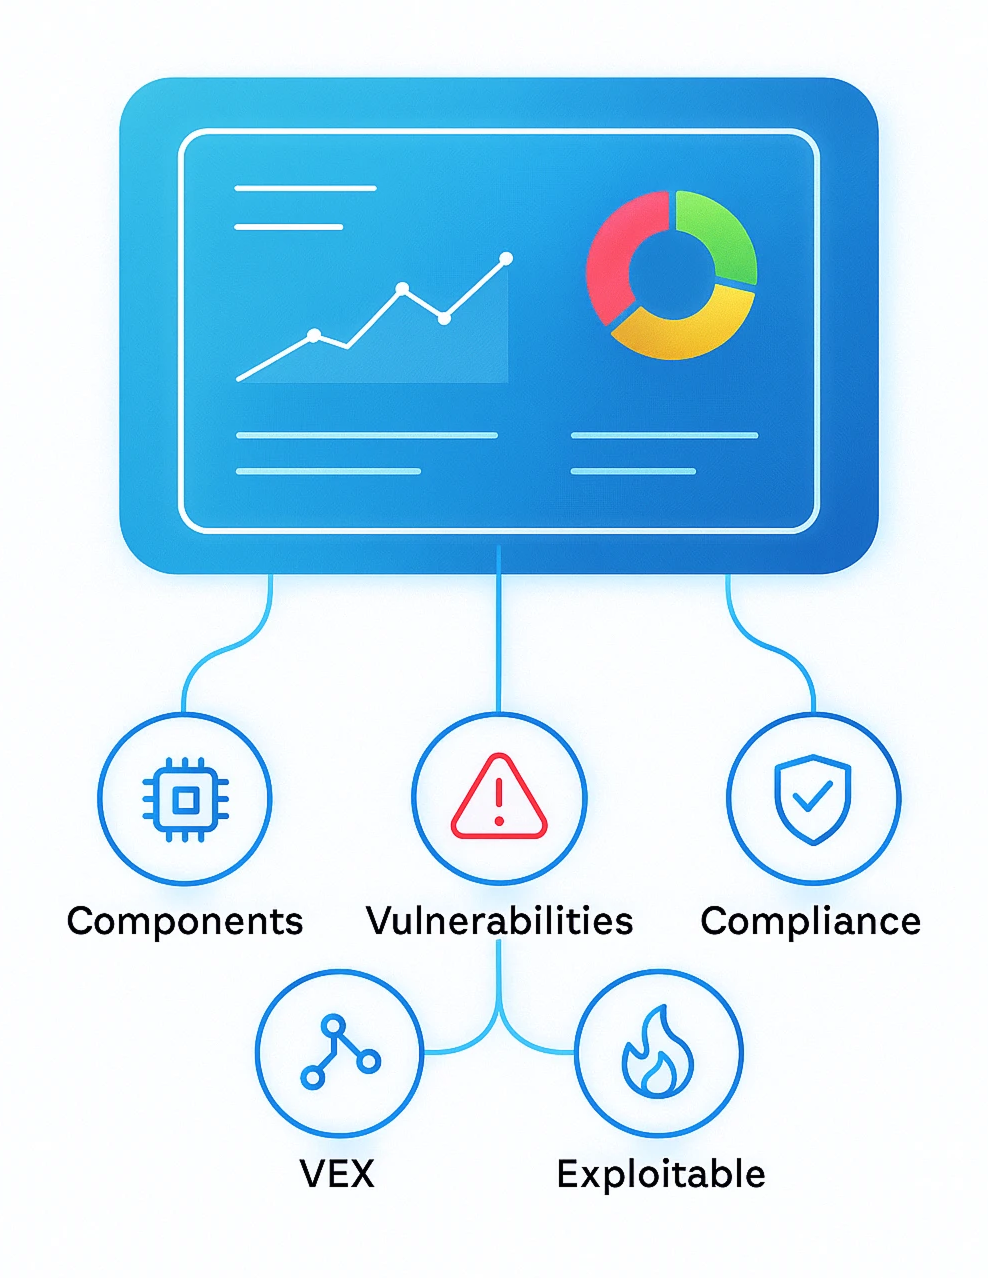
SBOM Studio understands the anatomy of every component in the SBOM, continuously enriches that component data, and tracks the vulnerabilities that may affect each and every one of them. You choose which projects you want monitored, and Cybeats rechecks them every hour. That is what an SBOM system of record adds.
Do you still need SBOM Studio if you run Dependency-Track?
Yes, and the difference is the data, not the feature list. Dependency-Track is an OWASP open source platform that ingests CycloneDX and matches components against public vulnerability sources. SBOM Studio ingests CycloneDX and SPDX, then does the work that makes supplier data usable: Quality Analysis flags issues in the component data you were sent, and Autocorrection repairs SBOMs that would otherwise be unusable.
Every component is then enriched from the Cybeats data lake with supply chain intelligence, and the whole thing is built to run at enterprise scale across thousands of Product Release SBOMs, with controlled sharing of each published one.

Which SBOM formats does SBOM Studio generate and ingest?
A commit generates CycloneDX 1.6 and 1.7 and SPDX 2.3 and 3.0.1. The ingestion range is wider, CycloneDX 1.2 through 1.7 and SPDX 2.2 through 3.0.1, so older supplier files still load.
A supplier who sends a component list as a CSV or an Excel sheet is not a dead end either. csv2cdx, the open source converter Cybeats builds and maintains, turns that spreadsheet into a valid CycloneDX SBOM you can ingest like any other. For the formats and data fields the EU CRA expects, see EU CRA SBOM requirements.
What if an SBOM has incomplete or broken component data?
Quality Analysis flags it, and Autocorrection repairs it. Quality Analysis reports issues in the component data an SBOM provides, and the Autocorrection repair modules Cybeats built over years let the platform ingest SBOMs that would otherwise be unusable. Studio and Consumer share both.
How often should an SBOM be updated?
Update an SBOM with every build or release, and revise it to correct any errors, as CISA's 2026 minimum elements recommend. SBOM Studio lets you update your Product SBOM as often as you need: every version is an immutable commit, nothing reaches customers until you publish it, and granular controls decide what each customer can access, from downloading the Product SBOM and VEX to view-only.
How do you publish a VEX document?
Generate it on demand and publish it as a separate file paired with the Product Release SBOM. The SBOM is immutable and says what the product contains. The VEX says which of those vulnerabilities are actually exploitable.
A VEX document is only correct as of the moment it was created. A new vulnerability can be reported minutes after you generate one, which is why VEX has to be treated as dynamic rather than a static artifact you file once and forget. SBOM Studio generates VEX on demand, and imports VEX from suppliers.
Which of your products are affected by a new CVE?
Look up the CVE and SBOM Studio returns the product releases that ship the affected component. Every component in every monitored project associated with your product releases is matched against vulnerability intelligence, so you get specific products and versions back instead of a manual cross-reference.

What is the safest way to share an SBOM with a customer?
Through the SBOM Studio Sharing Portal, not an email attachment. Once an SBOM leaves as a file, you lose control of who has it, who forwards it and who read it. In the Sharing Portal, authenticated customers see only the published Product SBOMs you grant them, and granular controls decide whether each one can download the SBOM, see vulnerabilities and download VEX, or view only. Access is revocable at any time, and every action is logged.
For machine to machine exchange, support for the Transparency Exchange API, the OWASP specification being standardized in Ecma TC54, is at proof-of-concept stage.

Does the FDA require an SBOM for medical devices?
Yes, for cyber devices. Section 524B(b)(3) of the FD&C Act requires manufacturers to provide an SBOM covering commercial, open source, and off-the-shelf software components. FDA's February 2026 premarket guidance also asks for each component's level of support and end-of-support date.

How do you manage an AIBOM for an AI product?
The same way you manage an SBOM, with AI models and datasets in the catalog. SBOM Studio ingests AIBOMs in CycloneDX or SPDX, including files from the OWASP AIBOM Generator, then monitors and shares them under the same controls.
Does SBOM Studio support CBOM and HBOM?
Yes, both, so the software, AI, cryptographic and hardware inventory of every product lives in one platform instead of four. HBOM has dedicated hardware and driver catalogs, and CBOM a dedicated catalog for cryptographic assets.
A Cryptography Bill of Materials inventories the algorithms and keys a product uses, so you can find what is exposed to post-quantum risk before you have to migrate it. A Hardware Bill of Materials covers the chips, radios and processors the product runs on.

What is Magic Link and how does it complete an SBOM?
Magic Link helps complete an SBOM by adding the open source packages it is missing with nothing more than a package link. Paste a link from npm, Maven, PyPI, GitHub or ten other package sources, and it fetches the name, manufacturer, supplier and available versions, then adds your chosen version to the Package Catalog or a software version. Cybeats enrichment fills in missing fields where data exists, such as licenses, CPEs, hashes and end-of-life dates, and you see known vulnerabilities by severity, so you can assess a package at the design stage, before you build with it.
Want to learn more about vulnerability lifecycle management?
in vulnerability management.
identification, prioritization, and remediation.
effective vulnerability management processes.
By entering your email, you agree to receive marketing emails from Cybeats. You may unsubscribe from these communications at any time. View our Privacy Policy for more information.

SBOM Lifecycle Management

See Cybeats Security Platform in Action Today
We shortened our vulnerability review timeframe from a day to under an hour. It is our go-to tool and we now know where to focus our limited security resources next.


SBOM Studio saves us approximately 500 hours per project on vulnerability analysis and prioritization for open-source projects.