Investors Inquiry
Request a Demo

Download Product Brochure
Download Cybeats Marketplace Brochure
Download Product Brochure
SBOM Studio



Software Bill of Materials: SBOM Studio
Gartner estimates that upwards of 80 percent of modern software incorporates open source libraries (OSS) or components from third-party upstream suppliers into product design. These pre-made components increase productivity and shorten development time, but they also introduce risk into the final product. Like any software module, these ingredients can contain vulnerabilities that emerge over time, making the overall software product less secure and reinforcing the need for continuous risk monitoring.

At every stage of the software development lifecycle (SDLC), Cybeats can extract the characteristics and attributes from software SBOM, even without access to source code, to deliver deep insights into the quality and security of software components.
SBOM Studio is the Management Solution for your Software Security Lifecycle
Cybeats SBOM Studio is an enterprise-class solution that helps you understand and track third-party components that are an integral part of your own software. Use SBOM Studio to document what you have and where it came from, and plan for the maintenance that will prevent security posture degradation over the life of your software.

Key Features

Coming into effect for the sharing of SBOMs are Industry regulations which mandate fines for non-compliance or shut down operations completely.
The first step in mitigating these risks is the ability to inspect all the software that comes from suppliers into your supply chains. In industries where safety and security are paramount, it is not economically feasible to manually inspect all third-party files to ensure the quality of a multi-tier software supply chain.
The time is now to develop a business advantage by putting the systems in place to manage and share SBOMs.

Organizations have a need to iterate and deliver software rapidly. Software that would take up to a month to complete can now be automatically remedied within minutes with Cybeats. A documented SBOM provides the ability to forecast costs for cybersecurity over the product lifecycle and allows the business to properly budget and allocate resources to maintain an advantage over security threats.

Create transparency and build trust across your software supply chain by sharing SBOMs with customers and receiving SBOMs from technology providers. Immediately understand the risks inherent in your products and mitigate as needed.
Who Needs SBOM Studio?
SBOM Studio is a versatile solution with many levels of sophistication. It provides high level data and metrics for executives and managers and can go deep into the nuts and bolts for software developers. Who can benefit from using SBOM Studio?

Industrial control system (ICS) environments who need to reduce cyber risk to ICS infrastructure, and gain compliance with ICS cybersecurity standards.

Operational Technology (OT) operators looking to reduce intrusions and protect their systems from disruption.

Medical device manufacturers and healthcare delivery organizations like hospitals whose patients use life-saving devices with embedded software.

Developers, product managers, and security officers who must ensure the secure design and ongoing function of any software product, including code embedded in various hardware devices.

Company executives who want to thoroughly understand the risks inherent in their software products and future costs for maintenance.

Any entity that sells or plans to sell software products, equipment, or devices with embedded software to the U.S. military or a U.S. government agency (compliance with Executive Order 14028).

Enterprise organizations and government agencies that utilize software from external vendors.

Anyone who makes use of a software supply chain that isn’t under their full control.
SBOM Studio: frequently asked questions
Answers on how SBOM Studio manages Product Release SBOMs, immutable commits, formats and VEX.

What is SBOM Studio?
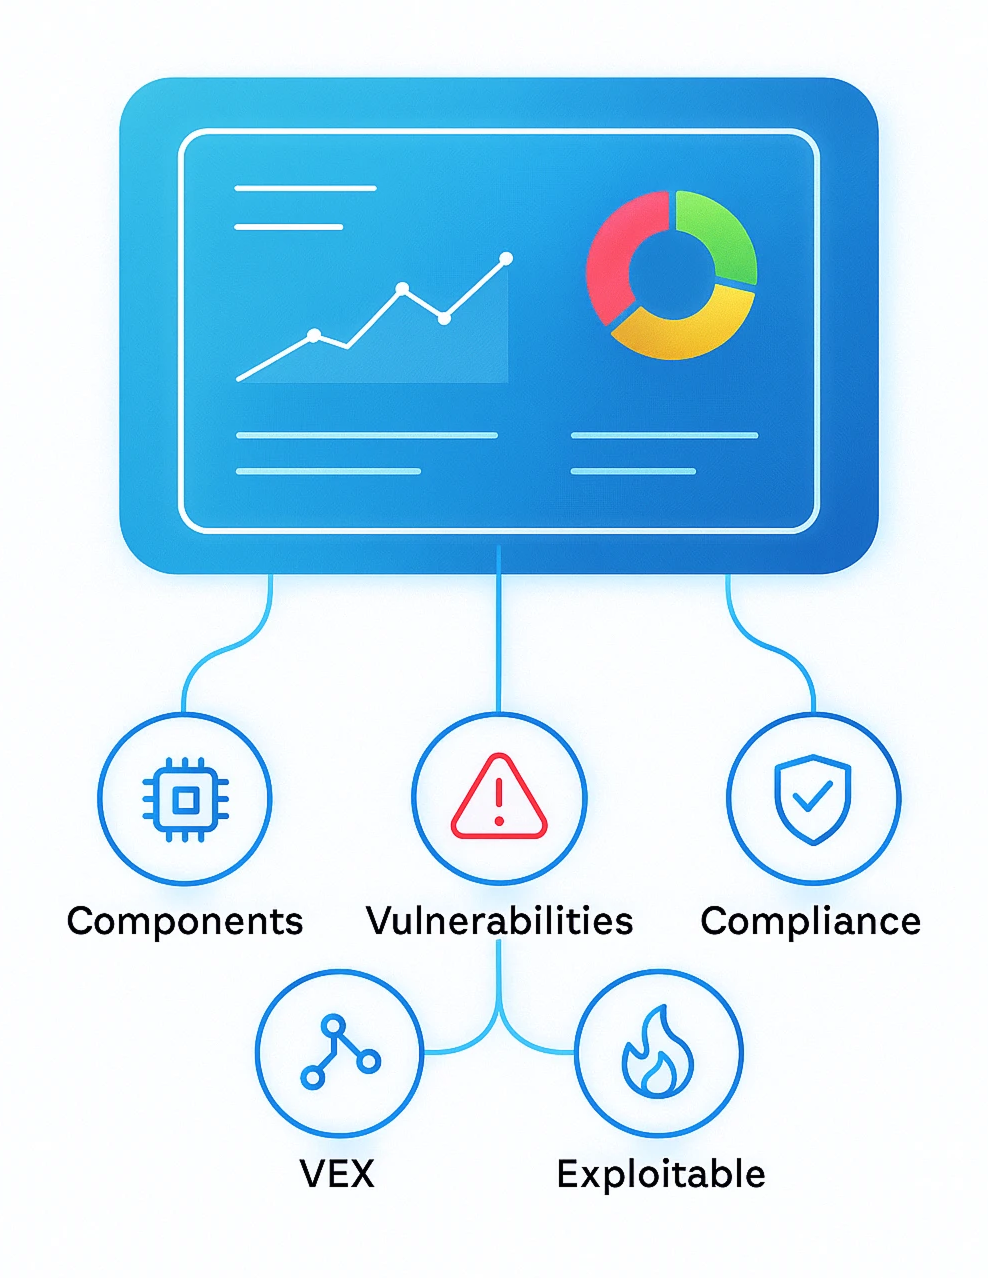
An SBOM management platform where the immutable commit is the compliance artifact. It records Product Release SBOMs as immutable commits, shows every component enriched with supply chain intelligence and the vulnerabilities that affect them, and controls who receives the published one.

Do you need an SBOM management platform if you already generate SBOMs?
Yes, because generating was never the hard part. Most teams already generate SBOMs, then park them in a repository, a shared drive or SharePoint and never look at what is inside them again. The file exists, the risk it describes goes unread.
SBOM Studio understands the anatomy of every component in the SBOM, continuously enriches that component data, and tracks the vulnerabilities that may affect each and every one of them. You choose which projects you want monitored, and Cybeats rechecks them every hour. That is what an SBOM system of record adds.
Do you still need SBOM Studio if you run Dependency-Track?
Yes, and the difference is the data, not the feature list. Dependency-Track is an OWASP open source platform that ingests CycloneDX and matches components against public vulnerability sources. SBOM Studio ingests CycloneDX and SPDX, then does the work that makes supplier data usable: Quality Analysis flags issues in the component data you were sent, and Autocorrection repairs SBOMs that would otherwise be unusable.
Every component is then enriched from the Cybeats data lake with supply chain intelligence, and the whole thing is built to run at enterprise scale across thousands of Product Release SBOMs, with controlled sharing of each published one.

Which SBOM formats does SBOM Studio generate and ingest?
A commit generates CycloneDX 1.6 and 1.7 and SPDX 2.3 and 3.0.1. The ingestion range is wider, CycloneDX 1.2 through 1.7 and SPDX 2.2 through 3.0.1, so older supplier files still load.
A supplier who sends a component list as a CSV or an Excel sheet is not a dead end either. csv2cdx, the open source converter Cybeats builds and maintains, turns that spreadsheet into a valid CycloneDX SBOM you can ingest like any other. For the formats and data fields the EU CRA expects, see EU CRA SBOM requirements.
What if an SBOM has incomplete or broken component data?
Quality Analysis flags it, and Autocorrection repairs it. Quality Analysis reports issues in the component data an SBOM provides, and the Autocorrection repair modules Cybeats built over years let the platform ingest SBOMs that would otherwise be unusable. Studio and Consumer share both.
How often should an SBOM be updated?
Every build or release, and again when the data changes. CISA's 2026 minimum elements say each software version or update should have an associated SBOM, and that a corrected error calls for a revised one. A Product Release SBOM can carry several immutable commits, with exactly one published.
How do you publish a VEX document?
Generate it on demand and publish it as a separate file paired with the Product Release SBOM. The SBOM is immutable and says what the product contains. The VEX says which of those vulnerabilities are actually exploitable.
A VEX document is only correct as of the moment it was created. A new vulnerability can be reported minutes after you generate one, which is why VEX has to be treated as dynamic rather than a static artifact you file once and forget. SBOM Studio generates VEX on demand, and imports VEX from suppliers.
Which of your products are affected by a new CVE?
Look up the CVE and SBOM Studio returns the product releases that ship the affected component. Every component in every monitored project associated with your product releases is matched against vulnerability intelligence, so you get specific products and versions back instead of a manual cross-reference.

What is the safest way to share an SBOM with a customer?
Through the SBOM Studio sharing portal, not an email attachment. Once an SBOM leaves as a file you lose the ability to say who has it, to withdraw it, or to prove who read it. The portal keeps that control: you decide who receives which SBOM and which VEX, each customer sees only their own products, access is revocable, and every access is logged.
For machine to machine exchange, Studio can serve the same SBOM and VEX over the Transparency Exchange API, the OWASP specification being standardized in Ecma TC54.

Does the FDA require an SBOM for medical devices?
Yes, for cyber devices. Section 524B(b)(3) of the FD&C Act requires manufacturers to provide an SBOM covering commercial, open source, and off-the-shelf software components. FDA's February 2026 premarket guidance also asks for each component's level of support and end-of-support date.

How do you manage an AIBOM for an AI product?
The same way you manage an SBOM, with AI models and datasets in the catalog. SBOM Studio ingests AIBOMs in CycloneDX or SPDX, including files from the OWASP AIBOM Generator, then monitors and shares them under the same controls.
Does SBOM Studio support CBOM and HBOM?
Yes, both, managed in the same catalog as your SBOMs. A Cryptography Bill of Materials inventories the cryptographic algorithms and keys a product uses, which is how you identify the assets exposed to post-quantum risk before you have to migrate them. A Hardware Bill of Materials covers the layer underneath: the chips, radios and processors the product runs on.
Studio manages all four bills of materials, SBOM, AIBOM, CBOM and HBOM, under the same enrichment, monitoring and sharing controls, so the software, AI, cryptographic and hardware inventory for a product sit in one place rather than four.

What is Magic Link and how does it complete an SBOM?
Paste a package manager or GitHub URL and Magic Link builds the component for you. It analyzes the source, creates the component in your catalog, and adds it to the product or project you choose. It also enriches incomplete component data and helps build Design SBOMs.
Want to learn more about vulnerability lifecycle management?
in vulnerability management.
identification, prioritization, and remediation.
effective vulnerability management processes.
By entering your email, you agree to receive marketing emails from Cybeats. You may unsubscribe from these communications at any time. View our Privacy Policy for more information.

SBOM Lifecycle Management

See Cybeats Security Platform in Action Today
We shortened our vulnerability review timeframe from a day to under an hour. It is our go-to tool and we now know where to focus our limited security resources next.


SBOM Studio saves us approximately 500 hours per project on vulnerability analysis and prioritization for open-source projects.